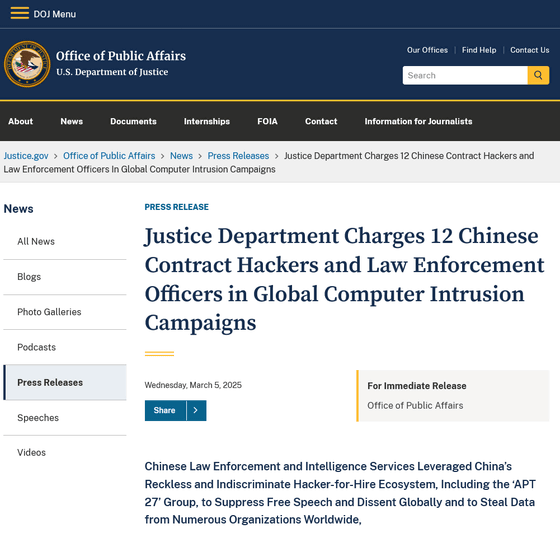
The U.S. Department of Justice has corrected a recent press release stating. That several federal agencies were "victims" of Chinese state-sponsored hacking, clarifying instead. That they were among the "targets" of a group tracked as QTFY. The change in wording, first reported by Reuters, significantly narrows the scope of. Confirmed compromise and underscores the fine line. Between attempted intrusion and successful breach. This guide covers DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims in detail. This guide covers DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims in detail. You can also read China Orders Massive Tesla Recalls Affecting Nearly 3 Million Vehicles Over Door Safety and Driver Monitoring.
DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims: What Changed in the DoJ Statement?
Originally, the DoJ's announcement listed NASA, the Federal Reserve, the Department of Energy, the Department of Justice itself, the Department of Health and Human Services, the National Institutes of Health, and the U.S. Senate as victims of "computer intrusion activity" by QTFY. In the updated version, those agencies have been reclassified as "among the targets of QTFY." A footnote attached to the release states: "Edits have been made to ensure this press release accurately reflects the government's allegations in the affidavit in support of the domain seizures."
How Does QTFY Operate?
According to the supporting affidavit, QTFY (also tracked as QT and QTCYBER) works on behalf of Nanjing Xinjiuwei Network Technology Co., a private Chinese company that has received payments from the Ministry of State Security (MSS). The group has operated since at least 2018 and has been described as. A "technical quartermaster" providing reconnaissance, proxy management. And operational routing to support Chinese cyber espionage. Two products anchor its toolkit: QScan, a vulnerability scanning and exploitation platform. And QTRouter, an obfuscation network. In one documented 2019 case, QTFY attempted to breach NASA by exploiting CVE-2019-11510. A critical Pulse Secure VPN flaw.

Why Does the FBI Seizure Matter?
The FBI has disrupted three domains tied to the operation, qtproxy[.]xyz, qt-proxy[.]org, and qt-team[.]com, effectively neutralizing QScan and QTRouter functionality. Lumen Black Lotus Labs research shows QTFY has industrialized Operational Relay Box (ORB) networks for PRC-linked espionage, building a decentralized botnet of compromised IoT devices and leased VPS instances that masks the origin of attacks. Nodes operated by the commercial Chinese proxy service fastlink[.]ws feed into Fast Labyrinth, an encrypted relay that blends malicious traffic with legitimate activity. As the affidavit alleges: "By routing their malicious internet traffic through IoT devices (compromised by QScan) local to their victims, these Chinese hackers can blend in with legitimate users and remain undetected when scanning and attacking critical infrastructure and other targets."
What This Means
The semantic shift from "victims" to "targets" is more than a legal formality. Attribution in cyber indictments must withstand courtroom scrutiny. And conflating attempted reconnaissance with confirmed data theft can undermine prosecutions. For CISOs at federal agencies and contractors, the case is a reminder. That exposure to a Chinese APT's scanning infrastructure does not equate to a confirmed breach. But it does demand continuous monitoring of edge devices, especially legacy VPN concentrators and IoT endpoints. That sit on flat networks.
What's Next
Expect further indictments as investigators map QTFY's customer base, since the group openly sells access to QScan and QTRouter. Defenders should audit outbound traffic for known indicators including qtproxy[.]xyz, qt-proxy[.]org, qt-team[.]com, and fastlink[.]ws, patch Pulse Secure VPN against CVE-2019-11510 if any unpatched instances remain, and segment IoT devices from operational techn Whether you are new to DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims or already experienced, the sections below have you covered.ology to limit ORB-style pivots. The DoJ has not indicated whether additional unsealed charges are imminent.
Key Points
DoJ corrected press release, reclassifying federal agencies as "targets" rather than "victims" of QTFY.
QTFY is linked to Nanjing Xinjiuwei Network Technology Co. and operates under MSS direction since 2018.
FBI seized qtproxy[.]xyz, qt-proxy[.]org, and qt-team[.]com domains tied to QScan and QTRouter.
The Bottom Line
The DoJ's clarification narrows the verified scope of Chinese compromise while reaffirming. That a sprawling IoT botnet, Fast Labyrinth, remains the central enabler of Beijing's stealth operations.
Related Resources
For more context, check our related article on this topic, related article on Apple Calendar Gets an AI-Powered Overhaul in iOS 27 with. Smart Event Details and Enhanced Siri Integration, related article on China Orders Massive Tesla Recalls Affecting Nearly 3 Million Vehicles. Over Door Safety and Driver Monitoring.